7
Article Rewrite:
Chrome Takes Steps to Address Recent ccTLD Registry Hijacks
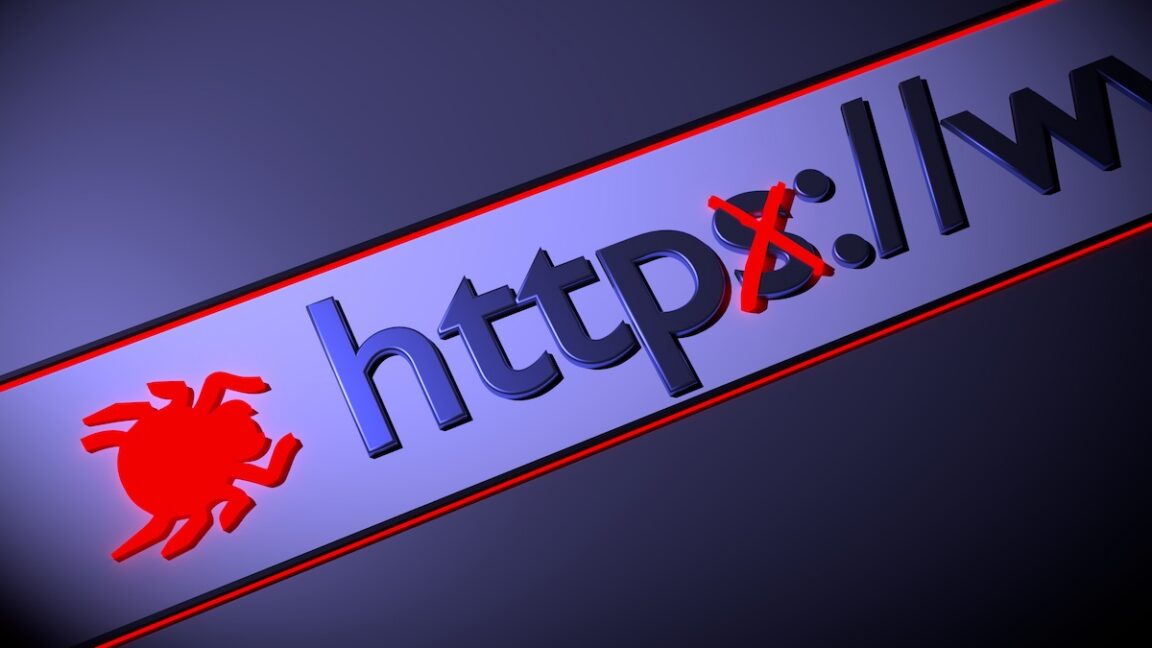
Following recent incidents of DNS hijacking affecting ccTLDs, Chrome has intervened to identify and block potentially fraudulent certificates. However, browser-side intervention alone cannot fully protect users from such threats.
It remains unclear which other organizations have been impacted, the number of unauthorized certificates issued, and whether all certificates, except those for Google domains, have been successfully blocked. Due to the slow and cumbersome process of revoking certificates officially, browser manufacturers have implemented quicker methods to block specific certificates at the browser level. While known unauthorized certificates have been blocked, the risk persists as undiscovered certificates continue to pose a threat.
Emphasizing that no compromise occurred to the affected domain owners’ infrastructure and that the certificate authority adhered to all requirements, Google disclosed that the attacker controlled three ccTLDs. This control enabled the attacker to manipulate the IP addresses of selected websites, change authoritative DNS records, and alter nameserver delegation for targeted domains. These actions facilitated passing industry validation checks that confirm domain ownership.
This incident echoes past instances where threat actors obtained fraudulent certificates, such as the 2011 hacking of a Netherlands-based certificate authority, DigiNotar. During that breach, fake certificates were created for Google.com and numerous high-traffic domains, impacting over 300,000 individuals with ties to Iran. Subsequent incidents have underscored the importance of domain owner and certificate authority vigilance in preventing such security breaches.
Source: arstechnica.com