

7
Router Manufacturers Seeking FCC Exemption Under Scrutiny
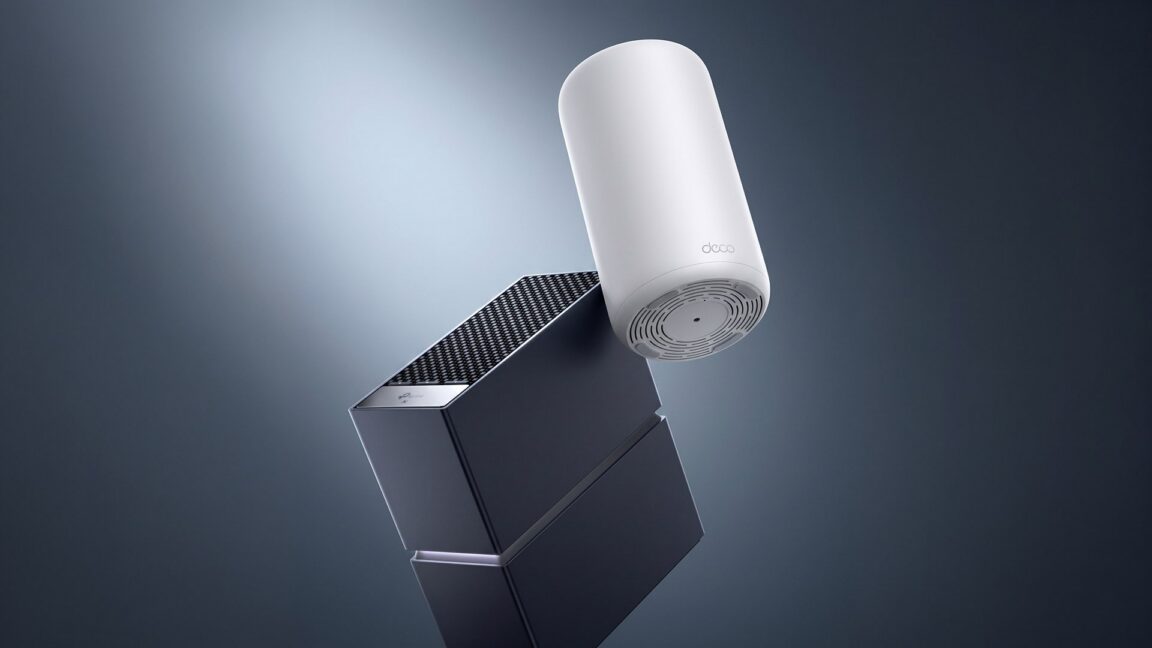
In the midst of a rise in high-profile cyber attacks linked to the Chinese government, router manufacturers like Netgear, Asus, and TP-Link are facing increased scrutiny. TP-Link, in particular, has come under fire for security vulnerabilities in its routers, leading to concerns about data privacy and potential exploitation by foreign entities.
TP-Link, a prominent router manufacturer, recently relocated its operations to the United States in 2024. However, the company’s move has not shielded it from controversy, as reports of compromised TP-Link routers being used in botnet attacks and data breaches have surfaced. The US intelligence agency has also pointed fingers at Russia’s involvement in exploiting TP-Link routers for cyber espionage activities.
In response to growing concerns, Republican lawmakers have called on the FCC to take a firm stand on router security. Despite TP-Link’s assurances about data encryption and storage practices, questions remain about the company’s ties to China and the potential risks posed by its routers. Republican state attorneys general have even taken legal action against TP-Link, alleging deceptive practices and security breaches that could benefit Chinese state hackers.
The scrutiny on TP-Link’s security practices has intensified, with a group of Republican state legislators joining the fray. In a letter to the FCC, they raised doubts about TP-Link’s claims regarding router security and independence from China. The legislators urged the FCC to address past violations and safeguard router users against potential exploitation by foreign entities, particularly the Chinese Communist Party.
As the debate over router security continues, TP-Link finds itself at the center of a contentious regulatory and legal battle. The outcome of these disputes will likely have far-reaching implications for the cybersecurity landscape and the protection of consumer data.
Source: arstechnica.com